Customers are the center of the operation at GetValidTest — a simple philosophy that means 24/7 staffing across time zones, verified FCP_FSM_AN-7.2 answers, and Fortinet FCP - FortiSIEM 7.2 Analyst material delivered the minute you need it.
Fortinet FCP_FSM_AN-7.2 Exam Syllabus Topics:
| Section | Objectives |
|---|---|
| Topic 1: Incident Detection and Response | - Incident workflow and management - Incident rules and alert configuration - Remediation actions and playbooks - Incident triggering and notification |
| Topic 2: FortiSIEM Overview and Navigation | - FortiSIEM architecture and components - CMDB (Configuration Management Database) concepts - GUI navigation and interface elements - User roles and permissions |
| Topic 3: Reporting and Dashboards | - Custom report creation - Report scheduling and distribution - Built-in report templates - Dashboard widgets and views |
| Topic 4: Admin and Configuration | - License management - Device discovery and monitoring - System settings and maintenance - Collector configuration |
| Topic 5: Event Handling and Log Management | - Real-time event correlation - Event types and taxonomy - Event collection and processing - Log parsing and normalization |
Studying for FCP_FSM_AN-7.2 Without Paper and Without Borders
- Incident Detection and Response ()
- Reporting and Dashboards ()
- Admin and Configuration ()
Fortinet FCP - FortiSIEM 7.2 Analyst Sample Questions:
Refer to the exhibit.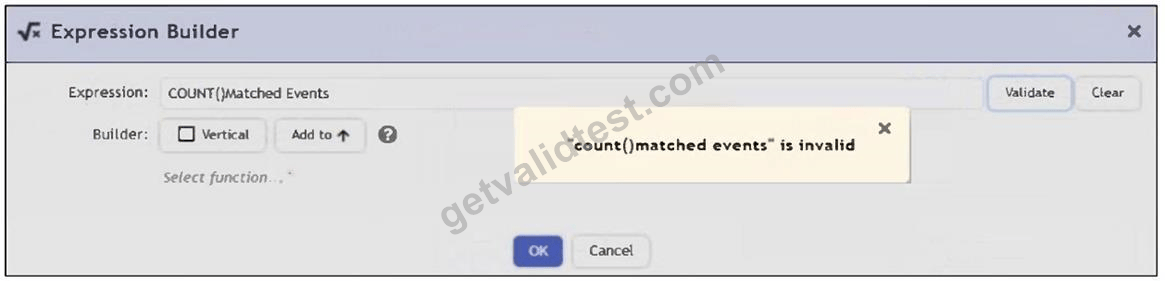
An analyst is trying to identify an issue using an expression based on the Expression Builder settings shown in the exhibit; however, the error message shown in the exhibit indicates that the expression is invalid.
What is the correct syntax to create an expression that generates a total count of matched events?
- A. COUNT(Matched Events)
- B. Matched Events (COUNT)
- C. (COUNT) Matched Events
- D. Matched Events COUNT()
Correct Answer: A 🗳️
Explanation: Only visible for GetValidTest members. You can sign-up / login (it's free).
When FortiSIEM is configured to apply ZTNA tags, what is the order of events when an analyst wants to automatically block a ZTNA tagged host?
- A. FortiEMS tags host > FortiSIEM receives tag information > FortiSIEM tags host > ZTNA tags enforced on FortiGate
- B. FortiEMS tags host > FortiEMS receives tag information > FortiSIEM tags host > ZTNA tags enforced on FortiGate
- C. FortiEMS receives tag information > FortiEMS tags host > FortiSIEM tags host > ZTNA tags enforced on FortiGate
- D. FortiSIEM tags host > FortiEMS receives tag information > FortiEMS tags host > ZTNA tags enforced on FortiGate
Correct Answer: A 🗳️
Explanation: Only visible for GetValidTest members. You can sign-up / login (it's free).
Refer to the exhibit. If you group the events by Reporting Device, Reporting IP, and Application Category, how many results will FortiSIEM display?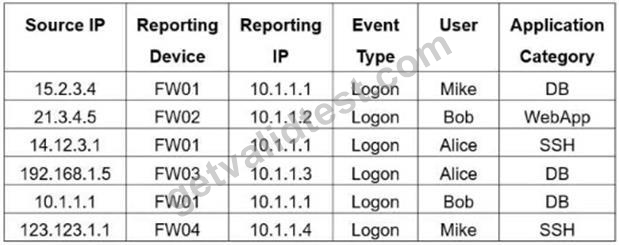
- A. One
- B. Two
- C. Five
- D. Six
- E. Four
Correct Answer: C 🗳️
Explanation: Only visible for GetValidTest members. You can sign-up / login (it's free).
Refer to the exhibit.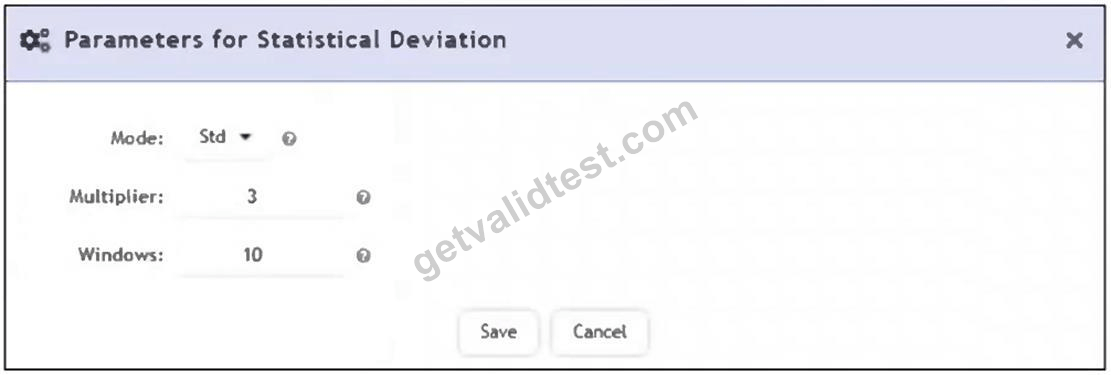
The exhibit shows the configuration for a machine learning dataset using anomaly detection.
If the report generating the data being analyzed is run every hour, how long must the FortiSIEM device be up before a valid training set can be produced?
- A. 10 hours
- B. 3 hours
- C. 24 hours
- D. 30 hours
Correct Answer: A 🗳️
Explanation: Only visible for GetValidTest members. You can sign-up / login (it's free).
Refer to the exhibit. Which section contains settings that determine which attribute associations are used to trigger an incident?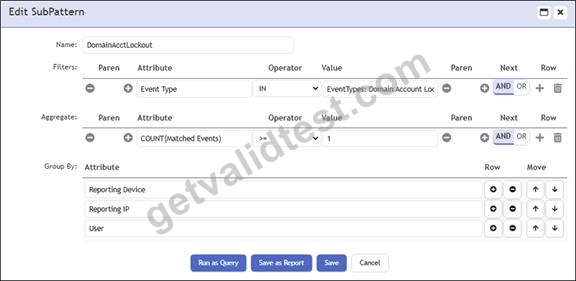
- A. Name
- B. Filters
- C. Aggregate
- D. Group By
Correct Answer: D 🗳️